Security
End-to-End Security for Connected Devices
We design and secure connected medical and consumer devices, from hardware through backend software.

What Sets Us Apart
Security in connected systems
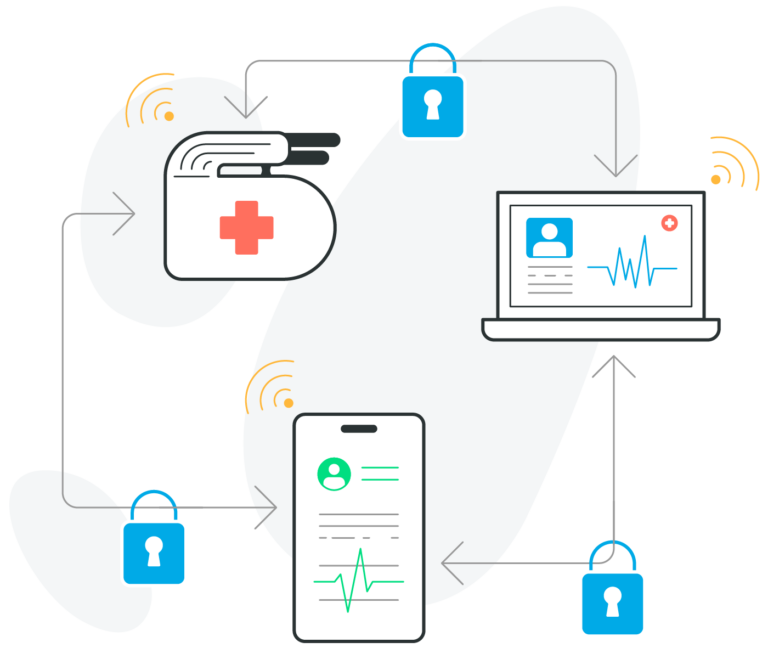
A Connected System has no single security perimeter.
Firmware, wireless protocols, mobile applications, and cloud backends each introduce a distinct attack surface. A decision made in one layer ripples through every other. Security that creates too much friction introduces its own risk: clinicians and end users route around it.
We design security across the full stack, from device hardware to backend systems, so controls hold together end-to-end.
The Result: A connected product where security is coherent across every layer, defensible under regulatory scrutiny, and built to hold up in the field.
WHAT WE SOLVE FOR
Security Vulnerabilities That Surface Late & Cost More to Fix
Security addressed one layer at a time leaves gaps where those layers meet. These are the ones we’re most often hired to close.

System Security Architecture
- Threat modeling absent from early design decisions
- Trust boundaries undefined across firmware, mobile, and cloud
- Security assumptions inconsistent between development teams
- Attack surface growing as system layers integrate
- Security review is happening too late to influence the architecture

Wireless & Protocol Security
- BLE pairing models that allow unauthenticated connections
- Control channels without session integrity or replay protection
- Protocol-level vulnerabilities exposing device to man-in-the-middle attacks
- Unencrypted data transmission across wireless links
- Weak authentication between device and mobile application

Device & Firmware Security
- Firmware running without signature verification or chain of trust
- Cryptographic keys stored in accessible flash memory
- Debug interfaces left exposed in production builds
- No rollback protection on firmware update paths
- Hardware attestation is absent from the device identity model
Compliance-Ready Cybersecurity
- Threat model not tied to design history file
- Cybersecurity documentation produced outside a Secure Product Development Framework
- Security risk management siloed from overall risk management process
- No documented PSIRT or post-market vulnerability response plan
- Security requirements not traced through design and verification

Provisioning & Identity Security
- Device identity not established or verifiable at manufacturing
- First-use pairing flows that can be spoofed or intercepted
- Credential issuance with no rotation or revocation strategy
- Provisioning process that breaks down at production scale
- Decommissioning flows are absent or incomplete
Purpose-Built Security At Every Layer Of A Connected Device
Each layer of a connected device has distinct security constraints, threat surface, and implementation requirements.
System Security Architecture
Security Requirements, Risks & Evidence
- Security risk management integrated with ISO 14971 and IEC 62304 processes
- SPDF-aligned security planning, requirements development, and evidence documentation
- Security requirements traceability
- Security control validation planning aligned to V&V strategy
Security Architecture & Design
- Threat modeling using STRIDE and MITRE frameworks for connected device systems
- Attack surface analysis across the full connected device ecosystem
- Authentication, authorization, and encryption architecture across device, mobile, and cloud
- Key and credential lifecycle design
- Privacy controls and data protection architecture
- Third-party and SOUP security assessment and vulnerability management
V&V & Post-Market Readiness
- Security verification strategy aligned to requirements and DHF
- Penetration test readiness and scope definition
- OTA and patch strategy for deployed devices
- Monitoring and logging architecture for post-market surveillance
- Vulnerability intake, triage, and response planning
Wireless & Protocol Security
Bluetooth Low Energy Security
- Pairing model selection and authentication design for medical and consumer devices
- Session integrity and replay protection on low-power wireless links
- Encrypted data transmission within BLE timing and throughput constraints
- Advertisement and scanning attack surface hardening
- Man-in-the-middle protection for device-to-mobile communication
Multi-Radio & Protocol Security
- WiFi authentication and certificate management for connected device environments
- Cellular authentication and SIM security considerations
- Coexistence security across multi-radio devices
- Protocol-level attack surface reduction across BLE, WiFi, and cellular
Firmware & Hardware Security
Boot & Firmware Integrity
- Secure boot and chain of trust on resource-constrained microcontrollers
- Anti-rollback version enforcement on firmware update paths
- Signed OTA update paths with staged rollout and rollback protection
- Memory protection and secure enclave configuration
Key Storage & Hardware Security
- Scalable, lightweight design systems built for long-term product evolution
- Native platform design systems supporting edge cases and long-term adherence
- Visual concepts converted into implementable, sequenced development plans
Hardening & Physical Security
- Debug interface hardening for production and post-market builds
- Tamper detection and physical attack resistance
- Binary protection against reverse engineering and extraction
Mobile Application Security
Device & Session Security
- Authenticated device pairing and session management for iOS and Android
- Jailbreak and root detection for regulated application environments
- Biometric authentication integration for device access and clinical workflows
- Binary protection and reverse engineering hardening
Data & Communication Security
- Secure local storage using platform Keychain and Keystore APIs
- Token lifecycle management for device control and cloud access
- Certificate validation and pinning for backend communication
- App transport security configuration
- PHI protection aligned to HIPAA and FDA privacy requirements
- Background data handling and process isolation
Backend Systems Security
Authentication & Data Protection
- API authentication and authorization for device and user identity
- Identity and access management aligned to clinical roles and workflows
- PHI encryption at rest and in transit across cloud infrastructure
- Access control and audit logging for regulatory traceability
- Secrets management for backend services and integrations
- Anomaly detection and intrusion monitoring for connected device fleets
- Dependency vulnerability scanning and patch management
Provisioning & Identity
- Device identity provisioning and credential issuance at manufacturing
- Credential rotation, revocation, and decommissioning across the device lifecycle
- First-use onboarding flows designed to resist spoofing and interception at scale
System Security Architecture
Security Requirements, Risks & Evidence
- Security risk management integrated with ISO 14971 and IEC 62304 processes
- SPDF-aligned security planning, requirements development, and evidence documentation
- Security requirements traceability
- Security control validation planning aligned to V&V strategy
Security Architecture & Design
- Threat modeling using STRIDE and MITRE frameworks for connected device systems
- Attack surface analysis across the full connected device ecosystem
- Authentication, authorization, and encryption architecture across device, mobile, and cloud
- Key and credential lifecycle design
- Privacy controls and data protection architecture
- Third-party and SOUP security assessment and vulnerability management
V&V & Post-Market Readiness
- Security verification strategy aligned to requirements and DHF
- Penetration test readiness and scope definition
- OTA and patch strategy for deployed devices
- Monitoring and logging architecture for post-market surveillance
- Vulnerability intake, triage, and response planning
Wireless & Protocol Security
Bluetooth Low Energy Security
- Pairing model selection and authentication design for medical and consumer devices
- Session integrity and replay protection on low-power wireless links
- Encrypted data transmission within BLE timing and throughput constraints
- Advertisement and scanning attack surface hardening
- Man-in-the-middle protection for device-to-mobile communication
Multi-Radio & Protocol Security
- WiFi authentication and certificate management for connected device environments
- Cellular authentication and SIM security considerations
- Coexistence security across multi-radio devices
- Protocol-level attack surface reduction across BLE, WiFi, and cellular
Firmware & Hardware Security
Boot & Firmware Integrity
- Secure boot and chain of trust on resource-constrained microcontrollers
- Anti-rollback version enforcement on firmware update paths
- Signed OTA update paths with staged rollout and rollback protection
- Memory protection and secure enclave configuration
Key Storage & Hardware Security
- Hardware-backed key storage on resource-constrained devices without integrated security processors
- Secure element integration for credential and certificate storage
- Hardware security module integration where device architecture supports it
- Secure manufacturing provisioning at the firmware layer
Hardening & Physical Security
- Debug interface hardening for production and post-market builds
- Tamper detection and physical attack resistance
- Binary protection against reverse engineering and extraction
Mobile Application Security
Device & Session Security
- Authenticated device pairing and session management for iOS and Android
- Jailbreak and root detection for regulated application environments
- Biometric authentication integration for device access and clinical workflows
- Binary protection and reverse engineering hardening
Data & Communication Security
- Secure local storage using platform Keychain and Keystore APIs
- Token lifecycle management for device control and cloud access
- Certificate validation and pinning for backend communication
- App transport security configuration
- PHI protection aligned to HIPAA and FDA privacy requirements
- Background data handling and process isolation
Backend Systems Security
Authentication & Data Protection
- API authentication and authorization for device and user identity
- Identity and access management aligned to clinical roles and workflows
- PHI encryption at rest and in transit across cloud infrastructure
- Access control and audit logging for regulatory traceability
- Secrets management for backend services and integrations
- Anomaly detection and intrusion monitoring for connected device fleets
- Dependency vulnerability scanning and patch management
Provisioning & Identity
- Device identity provisioning and credential issuance at manufacturing
- Credential rotation, revocation, and decommissioning across the device lifecycle
- First-use onboarding flows designed to resist spoofing and interception at scale
The Standards, Frameworks & Methods We Work From
Security for connected medical and consumer devices requires fluency across regulatory standards, cryptographic implementation, and connected device threat modeling.
Cybersecurity Guidance
Medical Device Security
Connected Product Security
Mobile & API Security
Consumer IoT Security
Secure Handshakes
Identity Provisioning & Lifecycle Management
Our Process
Security Engineered Into Every Phase of Development
Security stays coherent across the stack when each phase builds on the decisions made before it. Here’s how that looks in practice across a full engagement.
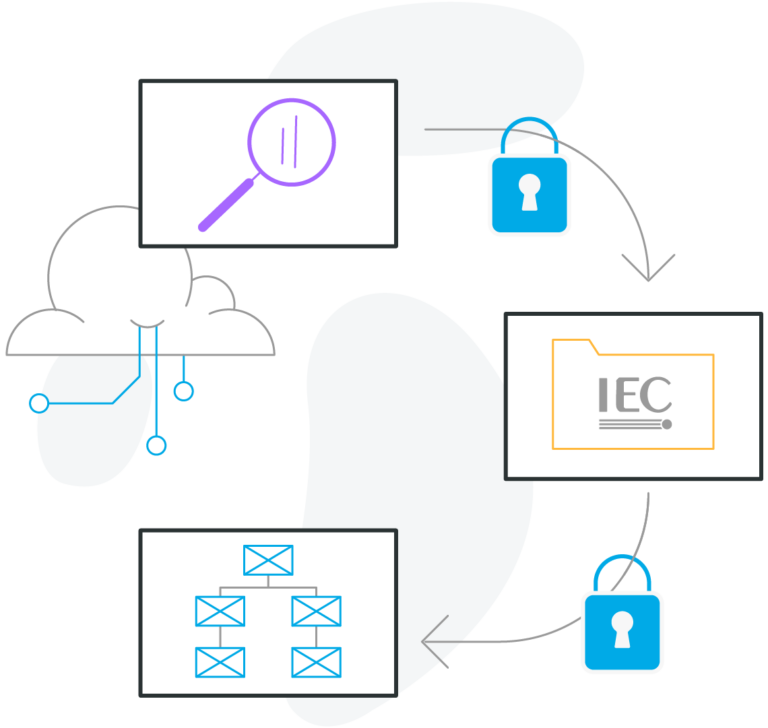
1. Discovery & Security Posture Review
2. Threat Model & Security Requirements
3. Architecture & Design
4. Implementation & Hardening
5. Verification, Validation & Evidence
6. Post-Market & Vulnerability Management

What you get
Built to Defend at Every Critical Moment
Security built into the development process puts you in a fundamentally different position at submission, launch, and beyond.
A Defensible Regulatory Submission
We build threat models, security risk management, and SBOM with traceability for a complete Design History File (DHF). Cybersecurity evidence exists when the product is developed, not assembled retroactively.
Security Coherent Across the Full Stack
We define trust boundaries at the architectural level and implement controls at each layer, with verification evidence produced at each phase. Every layer holds up under scrutiny because every layer was designed in the context of the others.
Post-Market Defensibility Built In
We establish SBOM, patch strategy, vulnerability intake, and PSIRT documentation during development. The product remains defensible as threats evolve, dependencies age, and post-market surveillance requirements grow.
Security Carried Through Implementation
The engineers who define the security model implement it across hardware, firmware, mobile, and backend systems. Design intent and execution stay aligned with no translation layer between security architecture and the controls that actually ship.
Security Designed Around Real Workflows
We build authentication flows, pairing models, and access controls around clinical and end-user behavior. Security that creates excessive friction introduces its own risk.
Security Across Disciplines
Security Applied at Every Layer of the Stack
Security isn’t a parallel workstream. It’s embedded in how we architect firmware, design mobile apps, build cloud systems, and design hardware.

Systems Architecture
Electronics
Embedded Software

Mobile Apps

Web Apps & Backends
Security Architecture Across the Hardest Device Classes
Implantables, clinical platforms, and complex connected systems where the stakes made security non-negotiable.
Sleep Apnea Therapy, Connected From Body to Cloud
Inspire® is the first FDA-approved neurostimulation therapy for moderate to severe obstructive sleep apnea.
A small implant stimulates the nerve that controls the tongue in time with the patient’s breathing, and a connected system sits around it, with a Bluetooth remote the patient holds, an app, and a clinician web portal that monitors the implant wirelessly.
For someone who could never live with a mask, that means sleeping with nothing on their face and starting therapy with a click. It also means the system around a Class III implant has moved through several device generations while every implant already placed stays in a body for years, so no part of the system can change without accounting for every implant in the field.


A Connected Care Platform Around an Implanted Insulin Pump
Portal Diabetes holds FDA Breakthrough Device designation for the Portal Pump™, an implantable insulin delivery system.
The pump is designed to sit in the abdomen, dose from a continuous glucose monitor with a heat-stable concentrated insulin, and take refills in a clinic after weeks or months.
For someone with type 1 diabetes, that means no carbohydrate counting, no meal announcements, and no waking in the night. It also means a loop that closes with no one in it, which has to be trusted before it is ever implanted and then stays in for five to seven years.

A Non-Invasive Cardiac Assessment Platform for Clinical Studies
Knowing how well a failing heart is pumping usually takes an echocardiogram and a trained operator, or a catheter threaded into the heart.
Sensydia’s Cardiac Performance System reads ejection fraction, cardiac output, and pulmonary artery pressure from disposable sensors on the chest, in minutes, at the bedside. Its ejection fraction measurement was first FDA-cleared in 2018, and the full platform holds Breakthrough Device Designation.
For a patient in an ICU or emergency department, that means answers without a referral or a procedure. It also means one measurement running across sensors, a gateway, a tablet, and the cloud, carrying patient data the whole way, while the platform is still being proven in clinical studies.

A Building Automation Concept Proven in the Real World in Weeks
A smart building startup is developing an automation platform for commercial buildings, one that controls and monitors dense fleets of connected devices across facilities shared by many tenants.
For a building operator, the aim is one system running the connected devices of an entire property. It also means radio working through metal enclosures and motor interference at extreme device density, and a security model that has to hold across every tenant, device, and door it touches.

An Implanted Therapy Its Clinicians Configure From Anywhere
A stealth-stage medical startup is developing an implanted neuromodulation therapy that its clinicians can adjust without the patient in the room.
For the patient, that means a therapy that changes when it needs to instead of at the next appointment.
It also means every adjustment travels from a clinician’s screen to a device inside someone’s body, and that path has to be trusted at Class III stakes before anything is implanted.
An Implant That Turns Thought Into Touchscreen Control
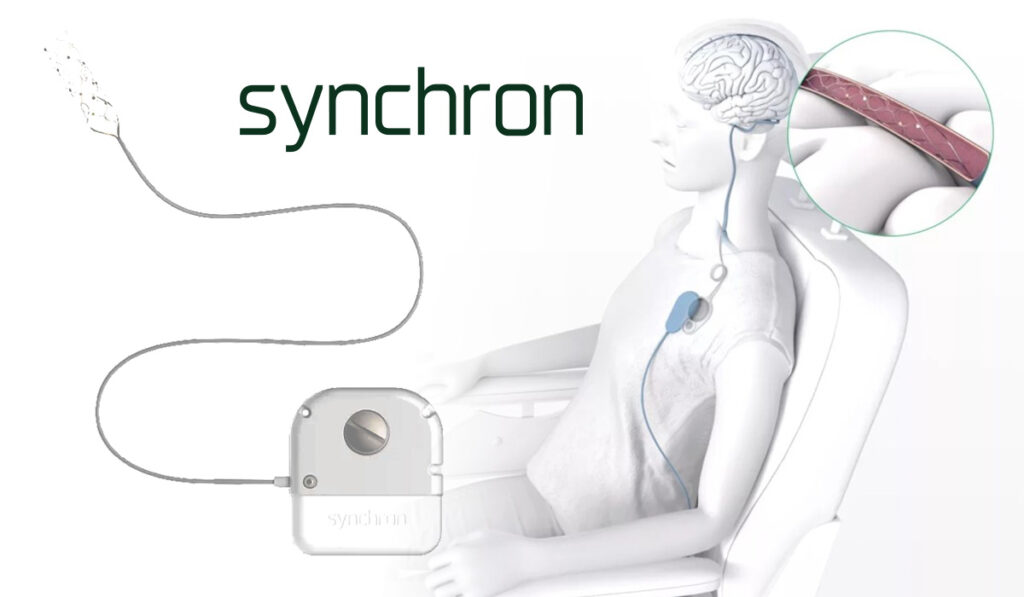
Synchron ran the first FDA-approved clinical trial of a permanently implanted brain-computer interface, and all six patients met the primary safety endpoint.
The Stentrode® is placed through a blood vessel, with no open brain surgery, and sits in a vein beside the motor cortex reading the intent to move.
For someone with severe paralysis, that means texting, browsing, and opening apps by thought alone. It also means the connection out of the body is the whole product, at Class III stakes. Nothing the implant does reaches a screen unless that link holds.
Sleep Apnea Therapy, Connected From Body to Cloud
A Connected Care Platform Around an Implanted Insulin Pump
A Non-Invasive Cardiac Assessment Platform for Clinical Studies
A Building Automation Concept Proven in the Real World in Weeks
An Implanted Therapy Its Clinicians Configure From Anywhere
An Implant That Turns Thought Into Touchscreen Control
Sleep Apnea Therapy, Connected From Body to Cloud
Inspire® is the first FDA-approved neurostimulation therapy for moderate to severe obstructive sleep apnea.
A small implant stimulates the nerve that controls the tongue in time with the patient’s breathing, and a connected system sits around it, with a Bluetooth remote the patient holds, an app, and a clinician web portal that monitors the implant wirelessly.
For someone who could never live with a mask, that means sleeping with nothing on their face and starting therapy with a click. It also means the system around a Class III implant has moved through several device generations while every implant already placed stays in a body for years, so no part of the system can change without accounting for every implant in the field.
A Connected Care Platform Around an Implanted Insulin Pump
Portal Diabetes holds FDA Breakthrough Device designation for the Portal Pump™, an implantable insulin delivery system.
The pump is designed to sit in the abdomen, dose from a continuous glucose monitor with a heat-stable concentrated insulin, and take refills in a clinic after weeks or months.
For someone with type 1 diabetes, that means no carbohydrate counting, no meal announcements, and no waking in the night. It also means a loop that closes with no one in it, which has to be trusted before it is ever implanted and then stays in for five to seven years.
A Non-Invasive Cardiac Assessment Platform for Clinical Studies
Knowing how well a failing heart is pumping usually takes an echocardiogram and a trained operator, or a catheter threaded into the heart.
Sensydia’s Cardiac Performance System reads ejection fraction, cardiac output, and pulmonary artery pressure from disposable sensors on the chest, in minutes, at the bedside. Its ejection fraction measurement was first FDA-cleared in 2018, and the full platform holds Breakthrough Device Designation.
For a patient in an ICU or emergency department, that means answers without a referral or a procedure. It also means one measurement running across sensors, a gateway, a tablet, and the cloud, carrying patient data the whole way, while the platform is still being proven in clinical studies.
A Building Automation Concept Proven in the Real World in Weeks
A smart building startup is developing an automation platform for commercial buildings, one that controls and monitors dense fleets of connected devices across facilities shared by many tenants.
For a building operator, the aim is one system running the connected devices of an entire property. It also means radio working through metal enclosures and motor interference at extreme device density, and a security model that has to hold across every tenant, device, and door it touches.
An Implanted Therapy Its Clinicians Configure From Anywhere
A stealth-stage medical startup is developing an implanted neuromodulation therapy that its clinicians can adjust without the patient in the room.
For the patient, that means a therapy that changes when it needs to instead of at the next appointment.
It also means every adjustment travels from a clinician’s screen to a device inside someone’s body, and that path has to be trusted at Class III stakes before anything is implanted.
An Implant That Turns Thought Into Touchscreen Control
Synchron ran the first FDA-approved clinical trial of a permanently implanted brain-computer interface, and all six patients met the primary safety endpoint.
The Stentrode® is placed through a blood vessel, with no open brain surgery, and sits in a vein beside the motor cortex reading the intent to move.
For someone with severe paralysis, that means texting, browsing, and opening apps by thought alone. It also means the connection out of the body is the whole product, at Class III stakes. Nothing the implant does reaches a screen unless that link holds.
Security Requirements Aren't Getting Simpler
Quick Discovery Call
Team Consultation